The practitioner's playbook: what to do, in what order, and how to keep it running
Operational Blueprint
- Written for Purview engineers, security architects, compliance leads and the programme managers who coordinate them
- Covers the unified DSPM experience, GA in May 2026, which absorbs DSPM (classic) and DSPM for AI (classic)
- How to read it: sections 2–4 background, 5–9 the phased runbook, 10–11 limitations and troubleshooting, 12–15 the governance kit
- Conventions: portal paths read Purview portal > Solutions > …; prices are US list per user per month, confirm with your licensing partner
DSPM doesn't classify, label or block anything. It reads, scores and orchestrates
An aggregation and orchestration layer on top of DLP, Insider Risk Management, sensitivity labels and Data Security Investigations.
What data do we have? Where is it stored? Who can access it? How is it protected?
Weak classification or missing audit on the left means empty dashboards on the right. Signal layer feeds DSPM; DSPM launches enforcement.
Nine building blocks make up the DSPM console
Console Architecture
Posture page
Security Copilot prompts; key metrics; top objectives by risk; 30-day trend
Data security objectives
Outcome cards; remediation plans; one-click policies
AI observability
AI apps and agents (incl. Agent 365) active in the last 30 days; high-risk count; sensitive interactions
Asset explorer
Unlabeled or classified data by workload; Data Security Posture Agent
Data risk assessments
Default and custom oversharing checks: SharePoint, OneDrive, Fabric
Activity explorer
Events on labelled or sensitive content; AI activities tab
Remediation actions
Automatic policies; most from DSPM for AI
Reports
Sensitive data usage; labelling; policy usage; risky user and agent behaviour
Setup tasks
Config steps; (preview) Sentinel data lake for GCP, Snowflake and other non-Microsoft sources
Know the edges: what DSPM covers, and what it never will
Boundary Scope
M365 only for native asset scanning
Asset explorer Microsoft locations strictly mean M365. Third-party SaaS, GCP, Snowflake, and Databricks need Sentinel lake or partner signals (Varonis, Cyera, BigID, OneTrust).
Admin-reviewed enforcement
AI agents can remove public links and apply DLP, but every remediation remains admin-reviewed, audited, and controlled by human sign-off.
It will not build your taxonomy or replace engines
DSPM will not invent SITs or label taxonomies. DLP, auto-labeling, and IRM remain tuned in their own engines; permissions require site owners.
The licence is E5 plus three consumption layers that are easy to miss
Licensing Prerequisites
Base: Microsoft 365 E5 or Microsoft Purview Suite
Per user: DSPM portal, objectives, reports, asset explorer, default risk assessments.
Layer 1: Microsoft 365 Copilot licences
To see Copilot and agent interactions.
Layer 2: Azure pay-as-you-go (PAYG)
For non-Microsoft AI apps, with device onboarding, browser extension, Edge policy or SASE/SSE.
Layer 3: Security Compute Units (SCUs)
For the Posture Agent, with Security Copilot onboarded. Custom assessments and item-level scanning add an Entra app registration; Fabric adds Fabric admin API tenant settings.
Copilot in Fabric and Security Copilot interactions need enterprise Purview data governance; proactive AI insights need Data Security Investigations.
The price tags: $60 for E5, $21 gap from E3, $6 per SCU overage
Commercial Benchmarks
$60
Microsoft 365 E5 / user / mo
Increased from $57 on 1 July 2026. Existing customers transition upon commercial renewal.
$21
E3 ($39) to E5 upgrade delta
Gap per user per month. Alternatively, license the Purview Suite add-on on top of E3.
$30
M365 Copilot / user / mo
Only needed for the active user population whose AI interactions you need to track.
400 SCUs
Monthly pool / 1,000 E5 users
Capped at 10,000 SCUs. Monthly reset, no rollover. Overage runs at planned $6/SCU.
US list prices. Model consumption meters in the Azure pricing calculator prior to commit.
Cost it in six steps: 1,000 users moving E3 to E5 is $252,000 a year at list
Financial Modeling
1. Segment users by persona
High-risk data handlers, Copilot users, general staff, frontline.
2. Pick the licence per persona
E5, E3 + Purview Suite, or out of scope.
3. Count Copilot-licensed users
Users you need to monitor.
4. List third-party AI channels
Browser, SASE network, enterprise apps; each maps to a PAYG meter.
5. Estimate SCU demand
Scheduled Posture Agent runs × average SCUs per run vs your monthly pool.
6. Add services and people
Partner days, Purview engineer FTE, change and training.
Worked Example
$252,000
1,000 × $21 × 12 = $252,000 per year, before discounts and before offsetting tools E5 replaces.
Least privilege first: who gets which Purview role
Role-Based Access Control
Compliance Administrator
Primary Purview engineer role. Requires Exchange Organization Management or Compliance Management for the Activate Audit prerequisite step.
Data Security Viewers & Readers
Security Copilot and Posture Agent users need Data Security Viewers. Read-only analysts take Purview Security Reader.
Data Security AI Viewer & Content Roles
AI governance leads get AI Viewer or Entra AI Admin. Investigators need Data Security AI Content Viewer + Content Explorer Content Viewer.
Governance boundary warning
No default DSPM role reads raw prompt text or file contents. Administrative Unit admins cannot deploy one-click policies: keep one central unrestricted admin.
Five tenant checks before you open DSPM for the first time
Pre-Flight Verification
- Licences assigned and tenant region supported
- Unified audit on: Get-AdminAuditLogConfig should return UnifiedAuditLogIngestionEnabled True, else Set-AdminAuditLogConfig -UnifiedAuditLogIngestionEnabled $true
- Copilot licences assigned to monitored users
- Enterprise Purview data governance enabled for Copilot in Fabric and Security Copilot interactions
- PAYG billing linked to an Azure subscription and resource group if governing non-Microsoft AI apps
Data takes about a day to appear after the first visit; each gap found later costs another day.
Catch shadow AI at the endpoint: devices, browser, Edge, network, SDK
Ai Telemetry Ingestion
| Devices. Onboard Windows and macOS devices to Purview (Intune, Group Policy or Defender for Endpoint) to see and block sensitive pastes into third-party AI sites. | |
|---|---|
| Browser extension. Deploy the Purview browser extension to Windows users for IRM AI-site detection and endpoint DLP in Chrome. | |
| Edge policy. Apply the Edge configuration policy for inline DLP on AI apps in Edge. | |
| SASE/SSE. Optional SASE/SSE integration for network-level AI traffic detection. Purview SDK. Purview SDK for Entra-registered in-house AI apps. |
Deeper scanning needs privileged apps and a Posture Agent checklist
Privileged Configuration
M365 item-level scanning
Single-tenant Entra app. Graph application permissions: Application.Read.All, Directory.Read.All, Files.ReadWrite.All, SensitivityLabels.Read.All, Sites.ReadWrite.All, User.Read.All.
Admin consent and a client secret required. It can write to every site: vault the secret, set expiry reminders, monitor sign-ins.
Fabric assessments
App in a security group; federated credentials preferred. A Fabric admin enables the two service principal admin API settings, scoped to that group.
Posture Agent
Security Copilot onboarded with SCUs; M365 data sharing on; Purview plug-in on. Enable Security Copilot for Purview Audit and DSPM; enable the agent with users in a role group.
Five phases, four gates, one roadmap
Roadmap Overview
Phase 0
Weeks 0–2
Mobilise
Decisions, roles, prerequisites
Phase 1
Weeks 2–6
Discover
Audit-only baseline
Phase 2
Weeks 6–10
Assess and prioritise
Risk register, policies in simulation
Phase 3
Weeks 10–18
Protect and remediate
Enforce in a fixed order
Phase 4
Week 18 onwards
Operate and maintain
Cadence that stops posture sliding back
Each phase has entry criteria, numbered steps and exit criteria. Durations assume a mid-size tenant.
Make the expensive-to-reverse decisions first
Phase 0 · Mobilise
Scope & Content Access
Focus Phase 1 on M365 + Copilot + browser AI (leave partner connectors for later). Log DPO, HR, and Legal approvals for named prompt/file content viewers.
Label Taxonomy Discipline
Limit to 4–5 parent labels: Public, General, Confidential, Highly Confidential. Restrict sub-labels exclusively to distinct encryption requirements.
Enforcement Appetite & Worker Notices
Staged ladder: Audit > Warn with override > Hard block for Highly Confidential only. Check works council and employee monitoring requirements before IRM capture.
Retention & Admin Units
Align AI interaction retention with Teams/email schedules. Configure tenant-wide admin engineering with scoped read-only views per region.
Phase 0 in eight moves, with a clear exit bar
Phase 0 Execution
- Stand up governance: steering group monthly, working group weekly, RACI
- Assign roles and record who holds content-viewer rights
- Verify tenant prerequisites; raise device, extension and Edge policy changes now, they have the longest lead time
- Create app registrations if custom or Fabric assessments are in scope
- Inventory crown jewels: 20–50 SharePoint sites, Teams and Fabric workspaces with the most sensitive data, each with a business owner
- Inventory existing labels, auto-labelling, DLP, IRM and retention; DSPM skips default labels if labels exist
- Agree the KPI set and how each is measured
- Launch comms wave 1 to leadership
Exit: decisions signed, roles assigned, audit verified, endpoint changes scheduled, crown-jewel list with owners.
Switch DSPM on in audit-only mode and build the baseline
Phase 1 · Discover
First Launch & Idle Safeguards
Open Purview portal > Solutions > Data Security Posture Management. Accept setup tasks. Wait 24h for initial telemetry; default assessments take ~4 days. Warning: if no admin opens DSPM for 60 days, M365 refresh pauses.
Nine Audit-Only Discovery Policies
Deploy in test mode: sensitive info added to AI sites (DLP), AI site visits & risky usage (IRM), unethical behavior in AI apps (Communication Compliance).
Five Passive Collection Policies
Turn on collection for Copilot in Fabric, Security Copilot, Edge browser prompts, SASE/SSE feeds, and registered enterprise AI apps.
Privacy by Default
Collection policies do not capture prompt text unless explicitly edited. Reconfirm employee monitoring position before enabling IRM.
Phase 1 baseline: assess, close classification gaps, review AI usage
Phase 1 Execution
Default assessment: weekly, top 100 SharePoint sites by usage. Custom assessment for crown jewels and sites outside the top 100.
Item-level scan for up to 10 high-risk SharePoint sites (no OneDrive). Results are snapshots that expire after 30 days: Duplicate to re-run; export each as baseline evidence.
Limits: 200,000 items per location; counts unreliable above 100,000. Run the Fabric tab if in scope.
Identify tab for unscanned content; on-demand classification.
Custom sensitive info types tested in the SIT tester; Asset explorer for unlabelled data.
Record AI apps and agents active in 30 days, high-risk count and sensitive interactions; review top 20 agents.
Sample Activity explorer AI activities.
Exit: assessments complete, AI signals visible, KPI baseline accepted by the steering group.
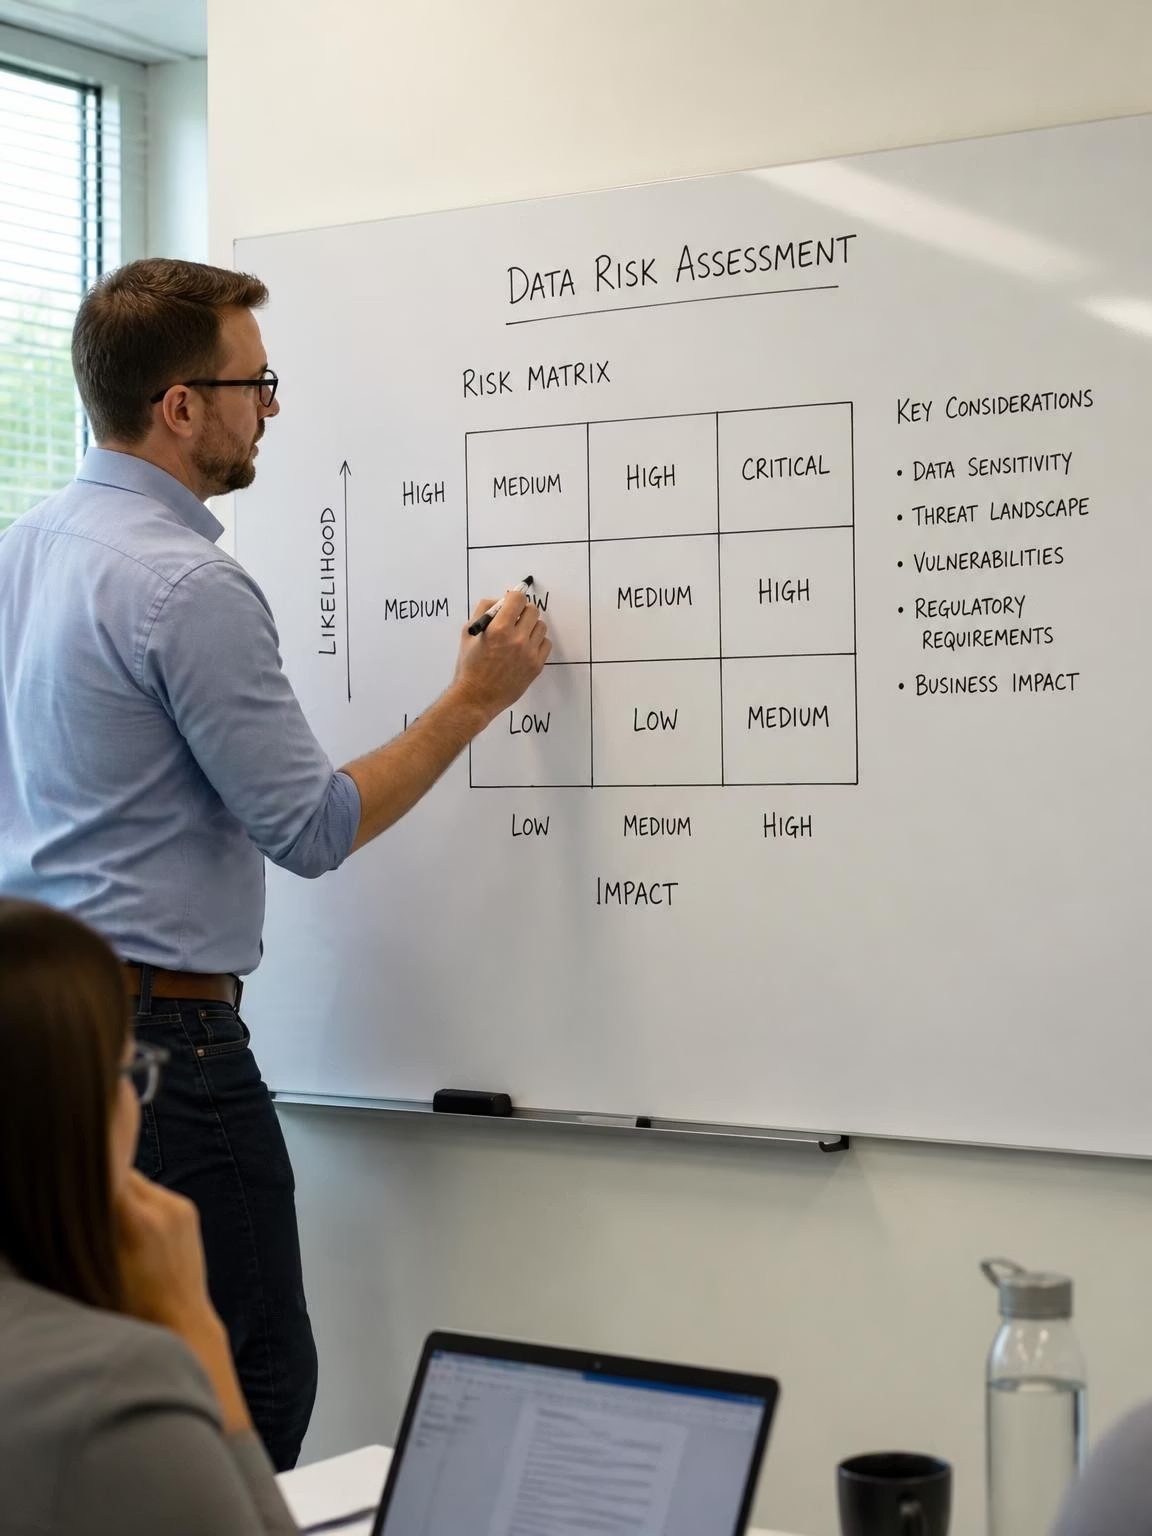
Score every risk: sensitivity × exposure × reach, maximum 27
Phase 2 · Assess
Sensitivity (1 to 3)
1: general only · 2: confidential or regulated in small volume · 3: Highly Confidential or regulated in bulk.
Exposure (1 to 3)
1: specific people · 2: org-wide links or large groups · 3: Anyone links, external sharing, broken inheritance.
Reach (1 to 3)
1: low activity and no AI access · 2: active site or some Copilot users · 3: top-100 site with heavy Copilot or agent use.
Record: location, score, finding, action, owner, fix-by date, status; review top 20 with owners. Map findings: sensitive unlabelled content → auto-labelling; labelled content Copilot shouldn't summarise → DLP for Copilot; whole site → Restricted Content Discovery; Anyone links → item-level remove link; stale content (3+ years) → retention delete; membership oversharing → site access review; sensitive AI pastes → endpoint/browser DLP + Adaptive Protection.
Design the labels, then rehearse every policy in simulation
Phase 2 Rehearsal
4–5 Parent Labels
Every extra label adds mislabelling and friction. Encrypt only where access must follow the file; test impact on search, co-authoring, eDiscovery and Copilot.
Default sharing link per label (Specific people for Confidential and above); container labels for Teams and sites; default labels for new content; justification to downgrade; reconcile existing labels.
Rehearse Every Policy
Auto-labelling: one policy per label, crown jewels first, simulate, tune SIT confidence and counts, re-simulate.
DLP for Copilot to restrict Highly Confidential, tested with a pilot group. Endpoint and browser DLP from the one-click “Block sensitive info from AI sites” policy (test mode, block-with-override for elevated-risk users). Edge inline DLP blocks unprotected browsers, so pilot first.
Exit: top 20 risks owned and dated; each policy has an accepted false-positive rate.
Label before you block, pilot before you broaden, warn before you block
Phase 3 · Protect
Strict policy rule: One change at a time with 5 working days between changes. Rollback DLP to simulation; never delete policies outright.
Fix oversharing with a runbook, and switch on AI protections
Remediation Workflows
Per item in Potentially overshared items: Resolve, Apply sensitivity label, Notify the site owner, or Remove sharing link. Prefer Notify with a fix-by date; remove links only for Highly Confidential items or after the date passes.
Whole sites: Protect tab options: DLP for Copilot, Restricted Content Discovery, auto-labelling, retention. Monitor tab for site access review; log actions and Duplicate the assessment to prove the reduction.
Protect sensitive data from Copilot processing: users lose Copilot help on those labels.
Block sensitive info from AI sites: block-with-override for elevated-risk users; turns on Adaptive Protection.
Block from AI apps in Edge: blocks unprotected browsers for in-scope users.
Approved AI list: publish before any block goes live.
Exit: KPI targets met on crown jewels, override rates in tolerance, no open P1 incidents.
Posture decays without a cadence
Phase 4 · Operate
Daily
SecOps triages DLP and IRM alerts.
Weekly
Default assessment: new top-100 sites and Anyone links; AI observability: new apps and agents; Activity explorer sample: confirm signals flow.
Monthly
Objective progress review; policy tuning; re-run custom assessments; SCU and PAYG check; KPI pack to the steering group.
Quarterly
Owner attestation; label taxonomy and SIT review; access review of Purview role holders; app secret rotation.
Semi-annual
Review Microsoft roadmap and message center; update the guide.
Every 60 days
Someone must open DSPM or data refresh pauses.
Run the Posture Agent smart, and keep SCUs and change under control
Agent Hygiene & Change Control
Agent scope & run
Natural-language search across SharePoint, OneDrive, Teams, Exchange and Copilot interactions for pre-investigation checks; formal cases stay in eDiscovery, Audit or Data Security Investigations. Run from DSPM > Discover > Asset explorer > Agent; add data sources first. Default window: 7 days; content up to 1 GB; no metadata filters. View Insights downloads to Word; activity is audited.
Prompt rules, SCUs & change management
Prompt rules. Include the UPN, quote full SIT or label names, state the date range (default 10 days, max 30), use one intent per prompt, use / in paths, and make prompts self-contained. SCUs. The monthly pool doesn't roll over; schedule recurring work, reserve 25% headroom for incidents, and review usage monthly. Change management. Every policy change is a change request with mode, scope, impact and rollback; re-simulate after SIT or label edits; onboard new sites, Teams and agents via checklist.
Twelve known limitations, and the workaround for each
Microsoft 365 only in Asset explorer: Sentinel data lake plus partner connectors; Purview Data Map for Azure data.
Item-level scan limited to SharePoint, 10 sites: rotate the slot; use SharePoint Advanced Management for OneDrive.
200,000 items per location: split assessments, treat counts as indicative.
Custom assessments are 30-day snapshots: duplicate monthly, keep exports.
Default assessment covers top 100 only: custom assessments for other crown jewels.
Notify email not customisable: send your own comms first.
AI events sometimes lack prompt text: check adjacent events, enable approved content capture.
Sensitive info event lacks user risk level: grant IRM Analyst to triage staff.
One-click policies need an unrestricted admin: central engineer creates, scope afterwards.
Refresh pauses after 60 days idle: weekly review.
Posture Agent preview, 7-day window, SCU-metered: always set date range and sources.
Edge inline DLP blocks unprotected browsers, and DSPM relies on labels and SITs you define: pilot scope; invest in custom SITs and on-demand classification.
"DSPM shows nothing"? It's almost always a missing prerequisite or role
Field Triage Runbook
Empty Dashboard or Results
Empty Posture page: Wait 24h on first visit, or check if 60-day idle pause triggered.
Default assessment empty: First run requires ~4 days. Custom results unchanged: Assessments are static snapshots; Duplicate and wait 48h.
Auth Failures & Policy Errors
Item-level auth fails: Verify the 6 Graph permissions, admin consent, and client secret expiry.
Fabric errors: Check service principal group & admin API settings. Can't create one-click policy: Admin unit restricted; needs unrestricted Compliance Admin.
Missing Signals & Browser Blocks
No Copilot data: Audit disabled or no licences. No third-party AI: Device onboarding, extension, or PAYG missing.
No prompt text: Add IRM/Content Viewer roles. Copilot unavailable: Enable plug-in & SCUs. Browsers blocked: Narrow Edge inline DLP scope.
Quick fix for audit: Set-AdminAuditLogConfig -UnifiedAuditLogIngestionEnabled $true. Deleted policies remain visible as PendingDeletion.
Programmes stall without owners: data owners fix, the programme lead is accountable
Governance & Accountability
Executive sponsor (CISO/CIO)
2 h a month · Scope, budget, enforcement appetite
Programme lead
0.5–1 FTE in rollout · Plan, register, KPIs, chasing owners
Purview engineer
1 FTE rollout, 0.5 BAU · Setup, assessments, policies
Compliance / DPO
0.25 FTE · Taxonomy, approvals, retention
Data and site owners
Per finding · Fix items, attest access
Operations
SecOps: triage and Posture Agent; endpoint/identity: devices, extension, apps; change and comms: 0.25 FTE; service desk: scripts and KB
RACI highlights: Sponsor accountable for scope and enforcement go-live; DPO accountable for content-access approvals and label taxonomy; Programme lead accountable for most other activities; Data owners responsible for remediation and attestation; SecOps accountable and responsible for alerts; Comms responsible for communications. One A per activity.
Eight comms waves, each tied to a technical milestone
Change Communications
T is the first enforcement change in Phase 3.
Phase 0, leadership: Why DSPM, scope, budget (Sponsor)
T-4 weeks, data and site owners: Your role and the Notify email (Programme lead)
T-3 weeks, works council / HR: AI capture and insider risk scope, formal consultation (Legal/HR)
T-2 weeks, all staff: Labels are coming, approved AI tools (Comms)
T-1 week, service desk: FAQs, override process, escalation
T, all staff: How to label, what blocks and warnings look like, email plus short video
T+2 weeks, site owners with findings: Your items, deadlines, how to fix (Purview engineer)
Monthly, steering group: KPI pack
Two emails, ready to send: all staff and site owners
Communication Templates
Protecting our data as we use AI: what changes on [date]
Files and emails carry labels; some sharing or pasting into unapproved AI tools may warn or block. Choose a label when prompted, use approved AI tools, read the FAQ, and contact the service desk.
Action needed by [date]: sensitive files shared too widely on [site]
Review the list, replace broad links with Specific people or remove access, and confirm site members. Expect the automated Purview email. After the date, links on Highly Confidential items are removed centrally.
Eleven KPIs, set only after the Phase 1 baseline
Metrics & Telemetry
Illustrative target attainment percentages. Target figures must be established only after Phase 1 baseline assessment completes.
The 11 Core Kpis
Data & AI Posture Telemetry
Data: Crown-jewel label coverage · Overshared sensitive sites · Anyone links on sensitive files · Unscanned content volume.
AI Usage: Sensitive AI interactions per 1k users · High-risk AI apps/agents count.
Enforcement: DLP override rate · Policy false positive rate · Median remediation days.
Operational: Objective progress · SCU pool consumption under 75%.
Four checklists: pre-flight, discovery, go-live, business as usual
Operational Runbooks
Licences, roles, content-viewer approvals, unrestricted admin, audit, Copilot licences, PAYG, devices, extension and Edge, app registrations, Security Copilot, monitoring position, crown-jewel list.
Setup tasks, audit-mode policies, assessments run, on-demand classification, AI signals validated, baselines stored.
Top 20 owned, labels piloted, simulation results and rollback notes, comms waves 4–6, approved AI list, one change every 5 days, before/after exports.
Weekly, monthly, quarterly and semi-annual tasks.
Start with the baseline: turn DSPM on in audit mode this month
Take Immediate Action
Built on Microsoft Learn pages last updated May–June 2026: Learn about DSPM, DSPM considerations, permissions, oversharing assessments, DSPM for AI considerations, Purview billing models.
Next step
Name a sponsor, verify audit, list your crown jewels.